Security Awareness Training: Explore Employee Education and Cyber Risk Reduction
Security Awareness Training helps organizations educate employees about common cybersecurity risks, safe digital practices, and responsible technology use. It covers topics such as phishing awareness, password security, social engineering, data protection, and incident reporting. Regular employee education can strengthen security awareness and help reduce avoidable cyber risks across workplace systems, devices, applications, and information.
Security Awareness Training: Explore Employee Education and Cyber Risk Reduction
Context
Security Awareness Training is an important part of modern cybersecurity programs because employees interact with digital systems, applications, email, files, and online platforms every day. While technical security controls can protect networks and devices, employees also influence how information is accessed, shared, stored, and handled.
Security Awareness Training focuses on building practical knowledge about cybersecurity risks and appropriate workplace behavior. Instead of treating cybersecurity as only an IT responsibility, it helps employees understand their role in protecting organizational information and digital resources.
Training programs commonly address phishing, social engineering, password protection, suspicious links, data handling, device security, and incident reporting. The exact subjects can vary according to the organization's technology environment, workforce, industry, and risk profile.
Common Training Areas
| Training area | Main focus |
|---|---|
| Phishing awareness | Recognizing suspicious emails, messages, and links |
| Password security | Strong authentication and account protection |
| Social engineering | Identifying manipulation and impersonation attempts |
| Data protection | Handling organizational and sensitive information appropriately |
| Device security | Safe use of computers, mobile devices, and removable media |
| Incident reporting | Reporting suspicious activity through appropriate channels |
| Remote work security | Safer practices when accessing workplace systems remotely |
| Physical security | Protecting devices, documents, and access credentials |
A useful training program should be understandable to employees with different levels of technical knowledge. Practical examples and realistic workplace situations can make cybersecurity concepts easier to recognize and apply.
Importance
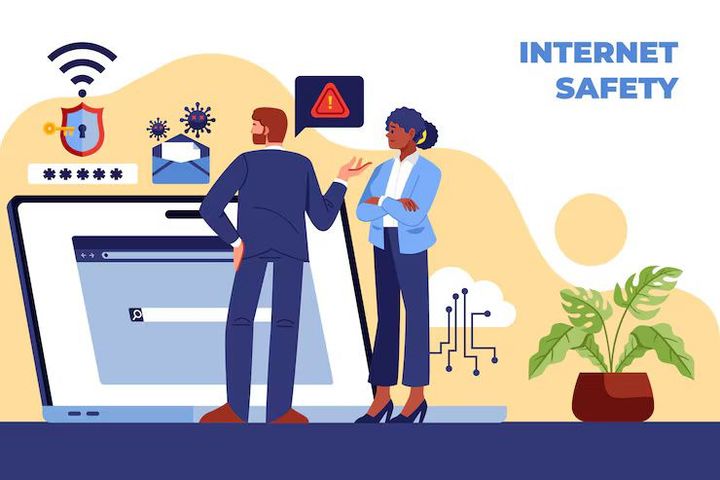
Employees can encounter cybersecurity risks through ordinary activities such as opening email attachments, accessing websites, sharing documents, using collaboration platforms, or responding to unexpected requests. Security Awareness Training helps employees recognize warning signs before an unsafe action creates a larger security problem.
One important area is phishing awareness. Fraudulent messages may imitate familiar organizations, colleagues, suppliers, or online platforms. Training can help employees examine sender information, links, attachments, requests for information, and unusual communication patterns.
Social engineering is another major training subject. Rather than relying only on technical vulnerabilities, social engineering attempts can manipulate people into revealing information or performing an action. Awareness programs can teach employees to pause, verify unusual requests, and follow established communication procedures.
Building Safer Digital Habits
Security awareness is more useful when it becomes part of everyday behavior. Employees can learn to use appropriate authentication methods, protect credentials, avoid sharing account information, verify unusual requests, and report suspicious activity promptly.
Training can also address information handling. Employees may work with customer records, financial documents, intellectual property, internal communications, or other organizational information. Awareness programs can explain appropriate storage, sharing, access, and disposal practices without requiring employees to become cybersecurity specialists.
Remote and hybrid work have also increased the importance of security awareness. Employees may connect through home networks, personal environments, mobile devices, or public locations. Training can cover secure access procedures, device protection, screen privacy, and appropriate use of organizational applications.
Measuring Awareness
Organizations can use several approaches to evaluate whether training is reaching employees effectively. Completion rates can show participation, while assessments can indicate whether employees understand key concepts.
Phishing simulations and other controlled exercises may also be used to evaluate how employees respond to realistic scenarios. These exercises should be designed as learning activities rather than as a way to embarrass individual employees.
Useful measurements can include:
Training completion rates
Assessment results
Reporting rates for suspicious messages
Results from controlled awareness exercises
Repeated areas of misunderstanding
Time taken to report suspected incidents
Participation in periodic awareness activities
Metrics should be interpreted in context. A single measurement does not necessarily represent the overall level of organizational security awareness.
Recent Updates
From 2024 through 2026, security awareness programs have increasingly adapted to changes in digital communication, artificial intelligence, cloud applications, and remote collaboration.
Generative AI has introduced new considerations for employee education. AI can make suspicious messages, documents, and impersonation attempts more convincing. Awareness programs therefore increasingly need to explain that polished writing, realistic images, or familiar-looking communication does not automatically establish authenticity.
Employees may also use AI tools for workplace tasks. Training can address organizational rules concerning confidential information, approved applications, generated content, verification, and responsible handling of data.
More Practical Training
Modern awareness programs are increasingly moving beyond a single annual training session. Short learning modules, periodic reminders, simulated scenarios, quizzes, and role-specific education can reinforce important behaviors throughout the year.
Different employees may also face different risks. Finance teams, administrators, developers, executives, customer-facing personnel, and technical teams may interact with different types of information and systems. Role-based awareness can therefore make training more relevant.
Security Culture
Organizations are also placing greater emphasis on security culture. A strong security culture encourages employees to report suspicious activity without unnecessary fear or confusion.
Clear reporting channels are particularly important. Employees should know where to report unusual messages, suspected account compromise, accidental data exposure, or other security concerns.
Security awareness can also become part of broader security practices such as identity management, endpoint protection, incident response, data governance, and organizational risk management.
Laws or Policies
Security Awareness Training may support an organization's broader legal, regulatory, contractual, and internal security obligations. However, the exact requirements depend on factors such as industry, location, organizational activities, and the types of information being handled.
Some regulatory and industry frameworks include expectations related to security awareness, workforce responsibilities, information protection, or security training. Organizations should identify the rules that actually apply to their operations rather than assuming that one training model satisfies every requirement.
Internal policies are also important. Organizations may establish rules covering passwords, authentication, acceptable technology use, remote access, email security, data classification, mobile devices, cloud applications, and incident reporting.
Training should align with those policies so employees understand not only general cybersecurity concepts but also the procedures they are expected to follow.
Privacy Considerations
Employee training programs may involve records such as completion information, assessment results, or simulated exercise results. Organizations should consider appropriate privacy, access-control, retention, and governance practices when handling such information.
Security Awareness Training should therefore operate as part of a broader governance structure rather than as an isolated educational activity.
Tools and Resources
A range of technologies can support security awareness programs. Learning management systems can distribute training modules, track participation, and organize educational content.
Phishing simulation platforms can provide controlled exercises that help organizations evaluate employee responses to suspicious communication. Security teams can combine these results with other security indicators to identify areas that may need additional education.
Other useful resources include:
Learning management systems
Phishing simulation platforms
Security awareness portals
Online assessment tools
Incident reporting systems
Identity and access management platforms
Endpoint security platforms
Security information and event management systems
Internal security policy libraries
Cybersecurity awareness documentation
Technology alone does not create effective awareness. Training materials should be clear, relevant, regularly reviewed, and aligned with actual organizational procedures.
FAQs
What is Security Awareness Training?
Security Awareness Training is an educational program that helps employees understand cybersecurity risks and follow safer digital practices. It commonly covers phishing, social engineering, authentication, data protection, device security, and incident reporting.
Why is Security Awareness Training important?
Security Awareness Training helps employees recognize common cybersecurity risks and understand appropriate responses. It can strengthen security culture and reduce avoidable mistakes involving accounts, information, devices, and communication.
What topics are included in Security Awareness Training?
Common topics include phishing awareness, password and authentication practices, social engineering, data protection, remote work security, device protection, suspicious activity reporting, and organizational security policies.
How often should Security Awareness Training be conducted?
Training frequency depends on organizational risk, internal policies, regulatory expectations, workforce changes, and the nature of the technology environment. Many organizations combine periodic formal training with shorter awareness activities throughout the year.
How can organizations measure Security Awareness Training?
Organizations can evaluate completion rates, assessment results, reporting behavior, controlled phishing exercises, and recurring areas of misunderstanding. Measurements are most useful when reviewed over time and combined with other security indicators.
Conclusion
Security Awareness Training helps connect employee behavior with broader cybersecurity practices. By educating employees about phishing, social engineering, information protection, authentication, and incident reporting, organizations can build stronger everyday security habits. Regular education, practical exercises, clear policies, and appropriate measurement can help maintain awareness as technology and cyber risks continue to change.