GDPR Compliance: Explore Data Privacy Frameworks and Business Requirements
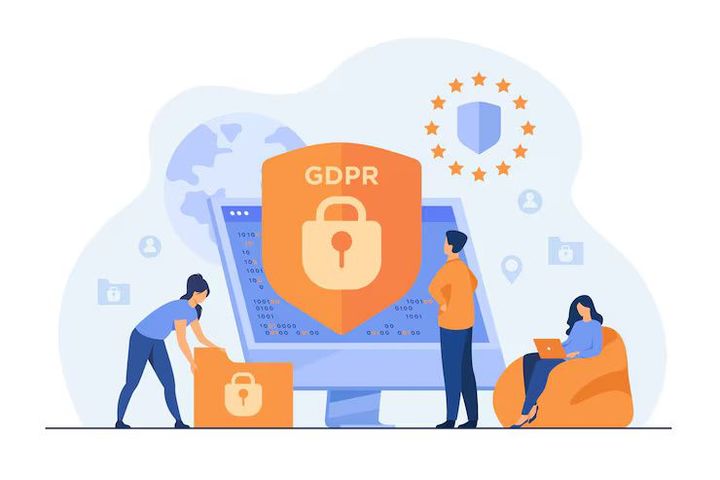
GDPR Compliance involves the policies, processes, and technical measures organizations use to protect personal data under the European Union’s General Data Protection Regulation. It covers areas such as data collection, processing, transparency, individual rights, security, documentation, and organizational accountability. This article explores GDPR requirements, privacy frameworks, business responsibilities, recent developments, and practical compliance resources.
GDPR Compliance: Explore Data Privacy Frameworks and Business Requirements
GDPR Compliance refers to the organizational, legal, and technical practices used to meet the requirements of the General Data Protection Regulation (GDPR). The regulation establishes rules for protecting personal data and gives individuals specific rights concerning how organizations collect, use, store, and otherwise process information about them.
The GDPR applies to organizations operating within the European Union and European Economic Area in circumstances covered by the regulation. It can also apply to organizations outside these areas when their processing activities fall within the regulation's territorial scope.
Personal data can include names, contact information, online identifiers, location information, identification details, and other information connected to an identifiable individual. Some categories of personal data receive additional protection under the regulation.
Context
The GDPR establishes a framework based on principles, lawful processing, transparency, individual rights, accountability, and appropriate security measures. Compliance is therefore broader than adding a privacy notice to a website.
Organizations need to understand what personal data they handle, why they process it, where it is stored, who can access it, and how it moves between systems or organizations.
Core GDPR Principles
The regulation establishes several important principles for personal-data processing.
| Principle | General Meaning |
|---|---|
| Lawfulness, fairness, and transparency | Processing should have a valid legal basis and be communicated clearly |
| Purpose limitation | Data should be collected for specified and legitimate purposes |
| Data minimization | Only appropriate data should be processed for the intended purpose |
| Accuracy | Personal data should be kept accurate and appropriately updated |
| Storage limitation | Data should not be retained longer than necessary for its purpose |
| Integrity and confidentiality | Data should receive appropriate security protection |
| Accountability | Organizations should be able to demonstrate compliance |
These principles influence how organizations design data processes, applications, forms, databases, analytics systems, and internal procedures.
Personal Data Processing
GDPR uses the term "processing" broadly. It can include collecting, recording, organizing, storing, changing, retrieving, consulting, using, sharing, restricting, or deleting personal data.
This means that many ordinary business activities can involve data processing, including customer records, employee information, website analytics, marketing databases, applications, and cloud platforms.
Controllers and Processors
A data controller determines the purposes and means of processing personal data. A data processor processes personal data on behalf of a controller.
The distinction is important because controllers and processors can have different responsibilities under the GDPR. Organizations should understand their role for each relevant processing activity.
Importance
GDPR Compliance is important because personal data is used throughout modern business operations. Organizations often rely on digital systems that collect and process information across websites, applications, customer platforms, cloud environments, and internal systems.
Transparency
Organizations need to provide appropriate information about how personal data is processed. Privacy information should be understandable and sufficiently clear for the relevant audience.
Transparency can include explaining the purposes of processing, relevant legal bases, data retention practices, individual rights, and other information required under the regulation.
Individual Rights
The GDPR provides individuals with several rights relating to their personal data. Depending on the circumstances, these can include rights to access, rectification, erasure, restriction of processing, data portability, and objection.
Some rights are subject to specific conditions and exceptions. Organizations therefore need processes for identifying, evaluating, and responding to requests within the applicable requirements.
Data Security
Organizations are expected to implement appropriate technical and organizational measures to protect personal data.
Security measures can include access controls, authentication, encryption, monitoring, secure development practices, backup procedures, staff awareness, and incident-management processes.
The appropriate controls depend on the nature and risks of the processing activity.
Accountability
GDPR Compliance includes the ability to demonstrate that appropriate privacy practices are in place. Documentation can therefore be an important part of a privacy program.
Organizations may maintain records of processing activities, policies, risk assessments, contracts, incident records, training materials, and other evidence relevant to their obligations.
Third-Party Processing
Organizations frequently use external platforms for hosting, analytics, communications, payments, customer management, and other activities. When personal data is processed by another organization, contractual and privacy responsibilities may arise.
Third-party relationships should therefore be assessed as part of an organization's overall data governance framework.
Recent Updates
From 2024 through 2026, GDPR-related developments have continued to involve regulatory enforcement, international data transfers, digital technologies, artificial intelligence, cybersecurity, and evolving privacy practices.
AI and Data Protection
The increasing use of artificial intelligence has created additional questions about personal-data processing, transparency, automated decision-making, data sources, and governance.
Organizations using AI systems may need to examine whether personal data is involved and identify the applicable GDPR responsibilities alongside other relevant technology regulations.
International Data Transfers
Cross-border transfers of personal data remain an important part of GDPR compliance for organizations using global cloud platforms, international vendors, and distributed operations.
Organizations may need to evaluate transfer mechanisms and applicable safeguards when personal data is transferred outside the European Economic Area.
Privacy by Design
Privacy considerations are increasingly incorporated earlier into technology and product development. Instead of addressing privacy only after a system has been created, organizations can consider data minimization, access controls, retention, transparency, and security during design.
This approach can reduce unnecessary data processing and make privacy requirements part of normal development processes.
Automated Decision-Making
Organizations using automated systems to make decisions involving individuals need to consider GDPR provisions concerning automated decision-making and profiling.
The applicability of specific requirements depends on the nature of the processing and its effects on individuals.
Regulatory Attention
Data protection authorities continue to focus on areas such as online tracking, international data transfers, children's data, cybersecurity, transparency, direct marketing, and large-scale processing.
Organizations should monitor guidance from relevant supervisory authorities because regulatory interpretation and enforcement priorities can change.
Laws or Policies
The GDPR is a European Union regulation, but its territorial scope can extend beyond organizations physically located within the EU. Determining whether the regulation applies requires examination of the organization's activities and processing circumstances.
Lawful Bases
Personal-data processing generally requires an applicable lawful basis. Depending on the situation, these can include consent, contractual necessity, legal obligation, vital interests, public task, or legitimate interests.
The appropriate basis depends on the actual processing activity. Organizations should not assume that one legal basis applies to all of their data processing.
Consent
Where consent is used as the lawful basis, it must meet GDPR requirements. Consent generally needs to be freely given, specific, informed, and unambiguous, and individuals may have the right to withdraw it.
Organizations should maintain appropriate records where consent is relied upon.
Special Categories
Certain types of personal data receive additional protection under the GDPR. These include information concerning areas such as health, biometric data used for identification, genetic data, political opinions, religious or philosophical beliefs, and other specified categories.
Processing these categories can require additional legal conditions beyond the ordinary requirements for personal data.
Data Breach Response
Organizations should have procedures for identifying, assessing, documenting, and responding to personal-data breaches.
Where required by the GDPR, a personal-data breach must be notified to the relevant supervisory authority within the applicable time requirement. Individual notification may also be required in circumstances involving a high risk to affected individuals.
Data Protection Impact Assessments
A Data Protection Impact Assessment, commonly called a DPIA, can be required when processing is likely to result in a high risk to individuals' rights and freedoms.
A DPIA can help organizations identify privacy risks, evaluate safeguards, and document decisions before high-risk processing begins.
Data Protection Officer
Certain organizations and processing activities require the appointment of a Data Protection Officer, or DPO. The requirement depends on factors such as the organization's activities and the nature and scale of processing.
A DPO can have responsibilities involving advice, monitoring, awareness, and cooperation with supervisory authorities.
Tools and Resources
GDPR Compliance programs often combine legal documentation, data-management tools, security controls, and organizational procedures.
Data Mapping
Data mapping helps organizations identify:
What personal data is collected
Where it originates
Why it is processed
Where it is stored
Who can access it
Which third parties receive it
How long it is retained
Where it is transferred
A data inventory can provide a foundation for broader privacy management.
Records of Processing Activities
Records of Processing Activities, or ROPA, can document relevant processing activities and the information required by the GDPR.
The level of detail and applicable requirements depend on the organization and its processing activities.
Privacy Management Platforms
Organizations may use privacy management software to organize data inventories, assessments, consent records, individual-rights requests, vendor reviews, and compliance documentation.
Technology can support privacy operations, but it does not replace legal analysis or organizational responsibility.
Security Controls
Common technical controls can include:
Identity and access management
Multi-factor authentication
Encryption
Network security
Endpoint protection
Logging and monitoring
Backup systems
Vulnerability management
Secure software development
Security controls should be selected according to the risks associated with the organization's processing activities.
Policies and Training
Organizations commonly maintain privacy and data-protection policies covering topics such as data handling, retention, access, incident response, third-party processing, and individual rights.
Staff awareness and role-specific training can help translate these policies into day-to-day practices.
FAQs
What is GDPR Compliance?
GDPR Compliance is the process of aligning an organization's personal-data processing activities with the requirements of the General Data Protection Regulation. It includes privacy governance, lawful processing, transparency, security, individual rights, and accountability.
Who needs to follow GDPR Compliance requirements?
The GDPR can apply to organizations in the EU and, in certain circumstances, organizations outside the EU when their processing activities fall within the regulation's territorial scope. Applicability depends on the specific activities involved.
What are the main GDPR Compliance principles?
The GDPR includes principles covering lawfulness and transparency, purpose limitation, data minimization, accuracy, storage limitation, security, and accountability.
What are GDPR individual rights?
Depending on the circumstances, individuals can have rights concerning access, correction, deletion, restriction, portability, objection, and certain forms of automated decision-making. Specific conditions and exceptions can apply.
Is GDPR Compliance only about cybersecurity?
No. Cybersecurity is an important part of GDPR Compliance, but GDPR also covers lawful processing, transparency, data minimization, retention, individual rights, documentation, contracts, governance, and other privacy responsibilities.
Conclusion
GDPR Compliance provides a structured framework for protecting personal data and managing privacy responsibilities. Organizations need to understand their processing activities, identify appropriate lawful bases, respect individual rights, implement suitable security measures, and maintain evidence of their privacy practices.
Recent developments have increased attention around artificial intelligence, international data transfers, automated decision-making, digital tracking, and cybersecurity. Effective privacy management therefore requires coordination between legal, technical, security, and operational teams while keeping practices aligned with the GDPR and relevant regulatory guidance.